Artificial intelligence has rapidly transitioned from a speculative technological curiosity to a foundational pillar of modern web architecture. As the digital landscape becomes increasingly complex, developers, web hosting providers, and site administrators are leveraging machine learning models to optimize costs, streamline operational efficiencies, and enhance customer service protocols. However, the most consequential application of this technology is currently unfolding in the sphere of cybersecurity. AI is fundamentally altering how vulnerabilities are identified, categorized, and mitigated, turning the tide in a long-standing arms race between security researchers and malicious actors.
The Evolution of Vulnerability Research
Historically, security research was a labor-intensive, human-centric endeavor. Expert researchers would spend weeks manually auditing source code, tracing execution paths, and identifying potential logic flaws or injection vulnerabilities. Today, the integration of Large Language Models (LLMs) and specialized security-focused AI agents has compressed these timelines from weeks to hours.
The shift is driven by the inherent capability of AI to synthesize vast repositories of programming documentation, such as PHP, JavaScript, and Python libraries, to recognize dangerous code patterns. Beyond mere pattern matching, modern AI models excel at performing cross-reference analysis. An individual code snippet may appear benign in isolation, but when evaluated alongside auxiliary dependencies or external input handlers, an AI model can identify complex, multi-stage vulnerabilities that often escape the notice of human auditors.
This capability has been validated in recent high-profile incidents. For instance, security researchers utilizing advanced LLM-based scanners have successfully unearthed critical vulnerabilities in major platforms that had remained undetected for over a decade. By simulating potential attack vectors across thousands of files simultaneously, these tools have demonstrated a level of efficiency that was previously impossible.
A Timeline of AI-Integrated Security
The integration of AI into the software development lifecycle (SDLC) has accelerated significantly between 2024 and 2026.

- Early 2024: Organizations began experimenting with AI-assisted code completion tools, which incidentally started flagging simple syntax-related security flaws.
- Late 2025: The adoption of specialized security models, such as those trained specifically on Common Weakness Enumeration (CWE) databases, began to permeate the open-source ecosystem.
- Mid-2026: Initiatives like the WordPress "Protect the Shire" program were launched. This project specifically utilizes automated AI agents to scan plugin submissions before they reach the public repository, effectively intercepting threats at the source.
- Present Day: The industry is moving toward "Security-as-Code" paradigms, where AI agents act as real-time gatekeepers during the CI/CD (Continuous Integration and Continuous Deployment) process.
The Paradox of Information Overload
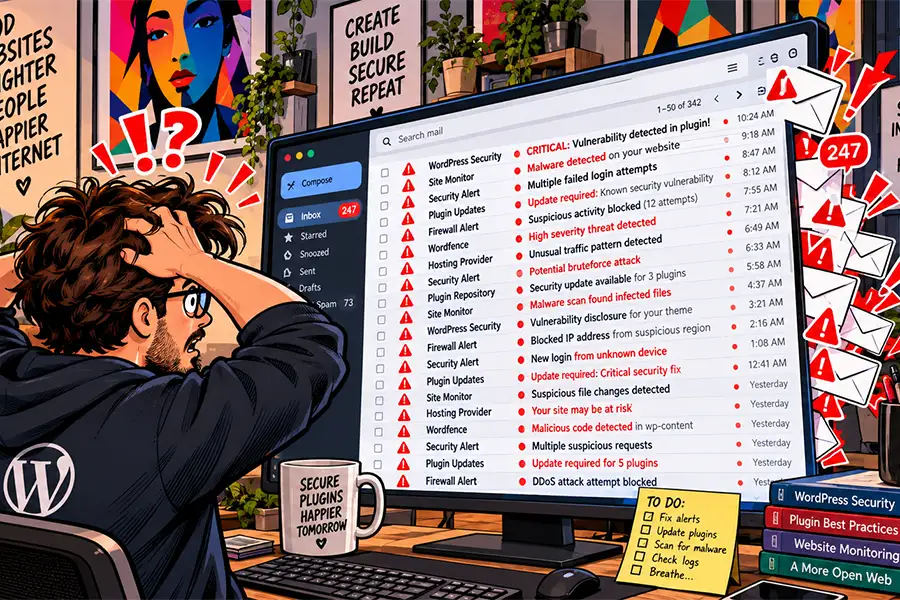
While the ability to find more vulnerabilities is objectively positive, it has created an unintended consequence: the "noise" of modern cybersecurity. According to recent industry reports, bug bounty platforms have seen a surge in report volume, with some programs experiencing a 500% increase in submissions compared to pre-AI periods.
This deluge of data presents a significant challenge for developers and site administrators. In a world where hundreds of potential vulnerabilities are flagged monthly, determining the priority of remediation becomes a complex task. Not every flagged issue poses an equal risk; however, once a vulnerability is disclosed publicly—often via automated security scanners—the window of opportunity for an attacker to exploit unpatched systems shrinks drastically.
This situation creates a "patch-or-perish" environment. For small to mid-sized businesses, the manual burden of verifying, testing, and deploying patches for every reported flaw is becoming unsustainable. The psychological and operational pressure on IT staff to monitor these disclosures 24/7 is a growing concern for industry analysts, who fear that "alert fatigue" may eventually lead to the oversight of truly critical threats.
Strategic Implications for Web Professionals
The proliferation of AI-driven security tools mandates a fundamental shift in how web professionals manage their infrastructure. Relying on manual updates or sporadic maintenance schedules is no longer sufficient to protect assets against automated, AI-augmented threats.
The industry is currently gravitating toward three main pillars of defense:
- Automated Patch Management: Agencies are increasingly adopting enterprise-grade auto-update systems. While these tools carry a risk of site instability, the alternative—leaving a site exposed to a known, exploit-ready vulnerability—is increasingly seen as the greater risk.
- Edge-Level Security: Rather than relying solely on the application layer, there is a strategic move to push security to the edge. Content Delivery Networks (CDNs) and web application firewalls (WAFs) are being configured to block traffic patterns associated with newly identified exploits, often before the underlying code has been patched.
- Collaborative Security Ecosystems: Organizations are recognizing that they cannot handle the volume of threats in isolation. There is a growing consensus that hosting providers must take on more responsibility. By implementing server-level monitoring and automated security patching at the platform level, hosting providers can shield their clients from the majority of automated threats.
Analyzing the Future: The AI Arms Race
The most significant long-term implication of this technology is the inevitability of the AI-on-AI conflict. As defensive AI becomes better at patching and identifying flaws, offensive AI—used by malicious actors—is becoming equally adept at discovering zero-day vulnerabilities and crafting polymorphic malware that changes its code signature to evade detection.

Industry experts note that the next generation of cybersecurity will be characterized by autonomous response systems. In this model, the software will not only identify a vulnerability but will also generate and test a functional patch, deploying it to production environments with minimal human intervention.
This evolution represents a "brave new world" for web professionals. While it promises a safer internet, it also shifts the role of the developer from a manual auditor to an architect of automated defense systems. The challenge will be ensuring that these automated systems remain transparent and controllable. If the tools used to secure our websites become too complex for human oversight, we risk creating a "black box" security model that could fail in unpredictable ways.
Conclusion: Preparing for the Shift
The adoption of AI in security research is not merely a trend; it is a structural change in the digital economy. The data is clear: AI finds more bugs, faster than ever before. For the web professional, the path forward involves embracing these tools to manage the increased volume of information while simultaneously advocating for more robust, platform-level security measures.
As we move forward, the goal must be the creation of an "immune system" for the web—a combination of AI-driven detection, edge-based mitigation, and automated patching that functions in the background, allowing human developers to focus on innovation rather than constant damage control. The transition will undoubtedly be turbulent, but it is a necessary evolution in the ongoing effort to secure the modern web.