The rapid integration of Artificial Intelligence into the web development ecosystem has fundamentally altered the landscape of digital security. Once a nascent experiment, AI now serves as a primary tool for developers, web hosts, and site administrators, driving cost reductions and operational efficiencies. However, the most significant shift has occurred in the realm of security research, where Large Language Models (LLMs) are being deployed to audit codebases for vulnerabilities at a velocity and scale previously unattainable by human analysts. This technological transition represents a double-edged sword: while AI provides a formidable shield against cyber threats, it simultaneously arms malicious actors with advanced capabilities to discover and exploit zero-day vulnerabilities.
The Chronology of AI-Assisted Security Research
The intersection of AI and web security has evolved rapidly over the past thirty-six months. Initial applications of AI in coding were largely limited to syntax correction and boilerplate generation. By 2025, the focus shifted toward security auditing. A pivotal moment in this timeline occurred in early 2026, when security researchers began utilizing specialized models—such as the OpenAI-derived "Sol Ultra"—to conduct deep-layer analysis of complex web architectures.
In June 2026, the WordPress community launched the "Protect the Shire" initiative, a systematic effort to integrate AI-driven static analysis into the plugin directory submission process. This move signaled a broader industry trend: moving from reactive patching to proactive, automated vulnerability detection. By late 2026, the industry saw the first major wave of security releases specifically credited to AI-assisted detection, where latent flaws—some dating back over a decade—were identified and remediated within hours of an automated scan.
The Mechanics of Algorithmic Vulnerability Detection
The efficacy of AI in security lies in its pattern recognition capabilities. Unlike traditional static analysis tools that rely on predefined rules, LLMs trained on vast repositories of PHP, JavaScript, and database documentation can synthesize the "intent" behind a block of code.
One of the most notable technical advantages of AI is its ability to identify cross-module vulnerabilities. Human auditors often struggle to correlate disparate code snippets that, while benign in isolation, create a catastrophic security loophole when executed in a specific sequence. AI models excel at mapping these logical dependencies. For example, a researcher might spend weeks manually tracing a data flow through an authentication plugin, only for an LLM to identify the logic gap in minutes. This capability is not merely an improvement in speed; it is a qualitative shift in how security teams perceive threat vectors.

Supporting Data and the "Bug Bounty" Explosion
The impact of this technology is clearly visible in the statistics provided by contemporary bug bounty programs. Data from the second half of 2026 indicates that platforms which previously averaged thirty to fifty vulnerability reports per month have seen an influx of over 450 reports.
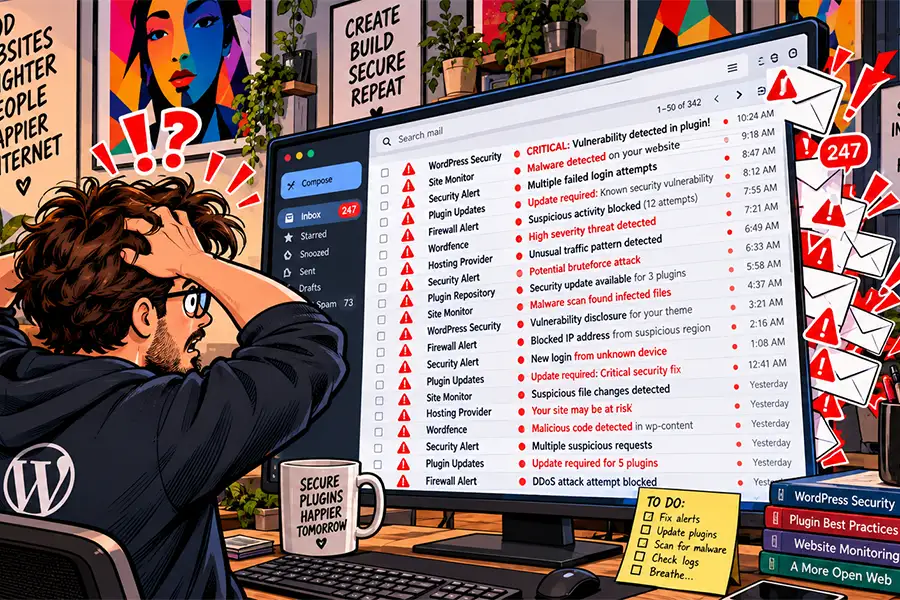
This surge is attributed to two factors: the democratization of security research and the efficiency of LLM-assisted scanning. While the high volume of reports validates the effectiveness of AI, it has also created an unprecedented strain on the ecosystem. Developers are now facing "vulnerability fatigue," where the sheer number of disclosed issues—many of which are edge cases requiring unlikely user behavior to exploit—threatens to overwhelm the capacity for timely patching.
Official Responses and Industry Sentiment
Industry leaders are divided on the long-term implications of this trend. Supporters, such as contributors to the WordPress security core team, argue that the "Protect the Shire" initiative is essential for the long-term viability of the open-source web. They maintain that the public disclosure of these flaws is a necessary price to pay for a more resilient infrastructure.
Conversely, some cybersecurity firms have expressed concern regarding the lack of triage standards. "The sheer volume of notifications is causing a degradation in incident response quality," noted one industry consultant. "When every minor bug is reported with the same urgency as a remote code execution exploit, the security professionals responsible for patching become desensitized, increasing the risk that a critical issue is buried under a mountain of noise."
Broader Implications for Web Professionals
For agencies, freelancers, and small business owners, the current environment presents a significant management challenge. The traditional model of periodic manual security updates is no longer sufficient. As AI-powered scanning becomes the standard for both white-hat researchers and black-hat attackers, the window between the discovery of a vulnerability and its weaponization is shrinking.
This shift has highlighted a critical need for structural changes at the hosting and infrastructure level. If individual site owners cannot keep pace with the influx of security patches, the responsibility must shift toward the providers. Content Delivery Networks (CDNs) and managed hosting environments are increasingly being positioned as the frontline of defense. By implementing automated Web Application Firewalls (WAFs) that can interpret security patches and deploy virtual shielding before a site owner has even seen the notification, these providers are providing a crucial buffer.

The Future of AI-Driven Defense
As we look toward the future, the integration of AI in security must move beyond simple detection. The next phase, already in development at several major web infrastructure companies, involves "self-healing" code. These systems would not only identify a vulnerability but also generate a tested, production-ready patch that can be deployed via a canary release process.
However, this future remains contingent on solving the "trust" problem. Automated patching carries the inherent risk of breaking site functionality, a prospect that terrifies many agencies managing mission-critical enterprise sites. The development of sophisticated, sandbox-based testing environments that can verify the integrity of a patch before it hits the live server will be the primary battleground for the next generation of web security tools.
Conclusion: Navigating the New Normal
The era of AI-assisted security is not a transient trend; it is the new baseline for the internet. While the technology has successfully brought to light hidden vulnerabilities that could have caused widespread damage, it has also introduced a layer of operational complexity that requires a fundamental rethink of web maintenance.
For web professionals, the path forward requires a transition from manual oversight to automated, platform-level security strategies. We must prioritize tools that offer intelligent triage and seamless, low-risk patching. The goal is to move beyond the current state of "information overload" toward a more nuanced, automated, and proactive security architecture. In this brave new world, those who successfully leverage AI to streamline their security operations will thrive, while those who rely on outdated, manual workflows will find themselves increasingly vulnerable to the very speed and intelligence that defines the modern web. The tools are available; the challenge now lies in our ability to manage them effectively at scale.