Artificial intelligence has rapidly transitioned from a speculative technological trend to a foundational pillar of modern web infrastructure. As organizations and developers grapple with an increasingly hostile digital landscape, the integration of machine learning models has become the primary mechanism for identifying, patching, and neutralizing vulnerabilities. This shift, while drastically increasing the efficiency of security research, has also created a paradoxical environment where the volume of reported threats threatens to overwhelm the very professionals tasked with managing them.
The evolution of automated security began in earnest as the complexity of web applications—particularly those built on content management systems like WordPress—outpaced the ability of human teams to audit them manually. Historically, security research was a laborious process of manual code review and heuristic analysis. However, the emergence of Large Language Models (LLMs) has fundamentally altered this timeline. By training these models on vast repositories of PHP, JavaScript, and framework-specific documentation, security firms have effectively automated the detection of common coding patterns that lead to exploits.
Chronology of an AI-Driven Security Paradigm
The current surge in AI-assisted security is the result of years of incremental progress in machine learning. In the early 2020s, static analysis tools were the industry standard; these programs looked for "known bad" code. By 2024, the industry saw the transition toward LLM-based analysis, which began to understand the intent and context of code segments.
A pivotal moment occurred in mid-2026, when researchers utilized advanced AI models to uncover vulnerabilities that had remained dormant for over a decade. These legacy bugs, often hidden in deep, intertwined dependency chains, were previously invisible to human auditors who lacked the capacity to map every potential execution path in a massive codebase. The discovery of these long-standing backdoors served as a wake-up call for the development community: if AI could find a decade-old vulnerability in a matter of hours, the barrier to entry for malicious actors had effectively collapsed.
In response, platforms like WordPress launched initiatives such as "Protect the Shire," a strategic effort to implement AI-based scanning directly into the plugin submission process. This proactive measure aims to catch security flaws before they ever reach the public, effectively moving the security perimeter upstream in the development lifecycle.
The Mechanism of AI-Enhanced Vulnerability Discovery
The primary strength of AI in this context is its ability to connect disparate, seemingly harmless code snippets. In modern web development, vulnerabilities are rarely found in a single, obvious function. Instead, they often arise from a "chaining" of events where input from one module passes through a series of transformations before hitting a sink where it can be exploited.

Humans are naturally limited by their cognitive load; they can only hold so many variables in their working memory. Conversely, an AI model can analyze the entire flow of a data request across thousands of lines of code. When the model identifies a path that could lead to unauthorized database access or remote code execution, it flags the issue for human review. This synergy—AI performing the "heavy lifting" of pattern recognition and human experts providing the final verification—has become the gold standard for security firms.
However, this technological leap is a two-way street. The same tools that allow researchers to harden software are readily available to cybercriminals. Attackers are increasingly using AI to perform automated reconnaissance on websites, searching for the very vulnerabilities that researchers have yet to report. This race between discovery and exploitation has created an environment where the time window between the announcement of a patch and its weaponization is shrinking to mere hours.
The Crisis of Information Overload
As the effectiveness of AI scanning increases, so does the sheer volume of reports. Data from prominent bug bounty programs illustrates this clearly. In 2025, a typical security program might have received 30 to 50 reports per month. By mid-2026, that number surged to nearly 500 per month.
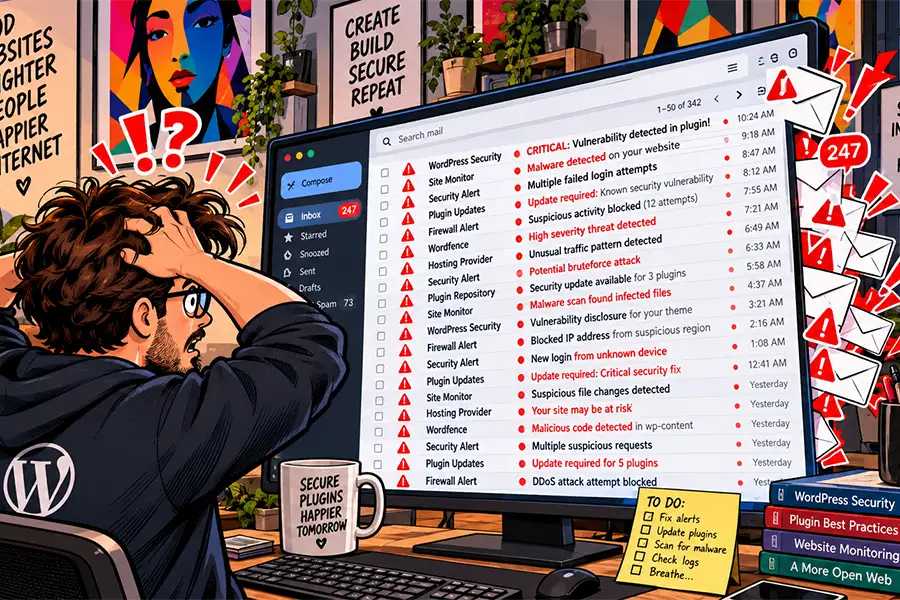
This deluge of data presents a significant challenge for web agencies and freelancers. When a security dashboard triggers dozens of alerts simultaneously, the human operator is faced with a triage dilemma: which of these vulnerabilities poses an immediate, existential threat, and which is a low-risk theoretical exploit?
The industry is currently struggling to differentiate between "critical" alerts and "noise." Many AI-generated reports flag theoretical issues that, while technically vulnerabilities, require a highly improbable series of user actions to trigger. Despite this, the public nature of these disclosures—often published on centralized security databases—forces developers to address every report to maintain compliance and public trust. This "alert fatigue" can lead to burnout among developers and, ironically, a decrease in overall security as teams begin to ignore or delay patching due to the sheer volume of incoming notifications.
Broader Implications and Future Strategy
The current trajectory suggests that the traditional model of manual patching and individual site management is reaching its breaking point. To survive in this new era, the industry must transition toward automated, systemic solutions that operate at scale.
Several strategies are currently being debated by industry leaders:

- Hosting-Level Mitigation: Rather than requiring individual site owners to manage patches, security responsibility is increasingly shifting to the hosting layer. By implementing Web Application Firewalls (WAFs) that are automatically updated with AI-derived threat intelligence, hosts can block exploits before they reach the application code.
- Infrastructure as Code (IaC): Agencies are moving toward standardized environments where security configurations are managed centrally. This allows for a "patch once, update all" approach that minimizes the time between the discovery of a vulnerability and the deployment of a fix.
- Collaborative Defense Networks: Initiatives that use AI to share threat intelligence across platforms in real-time are becoming vital. If an attack pattern is identified on one server, the intelligence is shared across the network to vaccinate other sites against the same vector.
Fact-Based Analysis of the Current Landscape
From a technical perspective, the reliance on AI for security is not a panacea. While AI excels at identifying syntax-based vulnerabilities, it still struggles with business logic flaws—errors in the way an application is intended to function. An AI might see that a piece of code is syntactically correct and secure, even if that code allows a user to perform an action they should not be permitted to do.
Furthermore, the rapid pace of development in the AI space means that security tools are in a constant state of flux. A model that is effective today may be circumvented by new obfuscation techniques tomorrow. The implication for web professionals is clear: technical literacy must evolve. The role of the developer is shifting from that of a manual coder to an orchestrator of automated security systems.
The psychological impact on the development community should not be understated. The constant pressure of "doomsday" security bulletins has created an atmosphere of perpetual anxiety. Agencies that once operated on a maintenance schedule of monthly updates now find themselves needing to be reactive on a daily, or even hourly, basis.
Conclusion: A New Era of Web Stewardship
The integration of AI into web security is an irreversible transformation. While it has granted researchers the power to clean up years of technical debt and secure the web at an unprecedented scale, it has also fundamentally altered the nature of the developer’s workload.
As we move forward, the success of the modern web will depend on our ability to build smarter, more resilient systems that can handle the volume of data AI provides. We must move away from the unsustainable model of manual, individual site intervention and toward robust, automated defenses managed by infrastructure providers. The goal is no longer just to build sites; it is to maintain a secure, automated ecosystem where the discovery of a vulnerability leads to a quiet, invisible patch, rather than a frantic, manual scramble for survival. The tools of the future are here, but they require a new level of maturity and systemic design to ensure they serve as protectors rather than agents of chaos.